
IEC 81001-5-1: What Medical Device Teams Need to Know
A practical guide to using IEC 81001-5-1 to build stronger medical-device cybersecurity lifecycle evidence without confusing a standard with a complete regulatory answer.
Read the guide -> Talk to an expert
TOPIC
Practical guidance for building cybersecurity into connected medical devices, from early development through post-market support.

A practical guide to using IEC 81001-5-1 to build stronger medical-device cybersecurity lifecycle evidence without confusing a standard with a complete regulatory answer.
Read the guide ->
A practical guide to connecting cybersecurity design, risk, testing, and lifecycle evidence for an FDA medical-device submission.
Read the guide ->
What cybersecurity certification can and cannot show, and how device teams can prepare the evidence a credible assessment requires.
Read the guide ->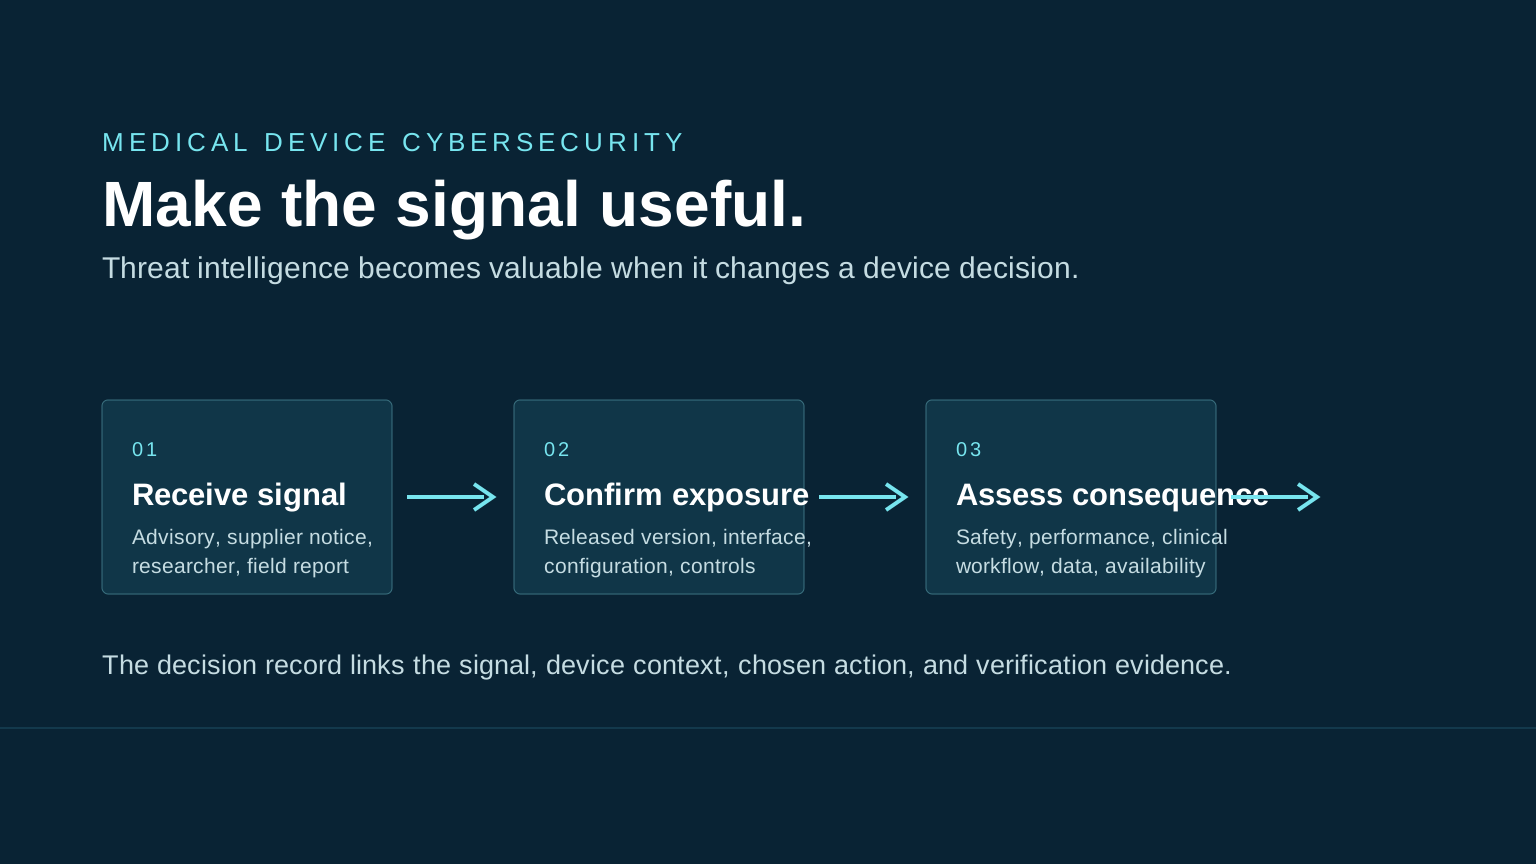
How medical-device teams can turn security advisories, supplier notices, and field signals into proportionate product decisions.
Read the guide ->
A practical guide to planning, running, and using medical device cybersecurity testing so results support real product, quality, and regulatory decisions.
Read the guide ->How medical-device teams can use cybersecurity standards, FDA guidance, quality systems, and risk management as one practical evidence trail.
Read the guide ->A practical guide to assessing medical device cybersecurity risk by connecting system context, exploitability, patient impact, controls, and lifecycle evidence.
Read the guide ->
How to build a medical device SBOM that supports FDA cybersecurity evidence, faster vulnerability decisions, and lifecycle control.
Read the guide ->
What medical-device teams should document to connect cybersecurity decisions, design evidence, risk management, and premarket readiness.
Read the guide ->
How to scope, run, and use medical device penetration testing to strengthen product decisions, evidence, and post-market readiness.
Read the guide ->
A practical guide to finding, prioritizing, documenting, and resolving medical-device cybersecurity vulnerabilities without losing sight of patient safety.
Read the guide ->
A practical way to define medical-device cyber risks, choose proportionate controls, and create evidence that holds together through development and review.
Read the guide ->
How medical-device teams can make cybersecurity part of product, quality, and regulatory planning before it becomes a submission or post-market problem.
Read the guide ->